By: Jay Kt
Here’s a conversation I’ve had with more merchants than I can count. They’ll say something like, “We use encryption, so we’re covered.” And technically, sure, the data is scrambled. But covered? That’s doing a lot of heavy lifting as a word.
Payment tokenization and encryption get lumped together constantly. Both protect card data. Both show up in PCI compliance conversations. But they work in completely different ways, and picking the wrong one (or worse, not understanding what you’ve picked) creates problems that don’t surface until something breaks. Or until an auditor shows up asking questions you don’t have clean answers for.
Encryption Protects Data. It Also Keeps You on the Hook.
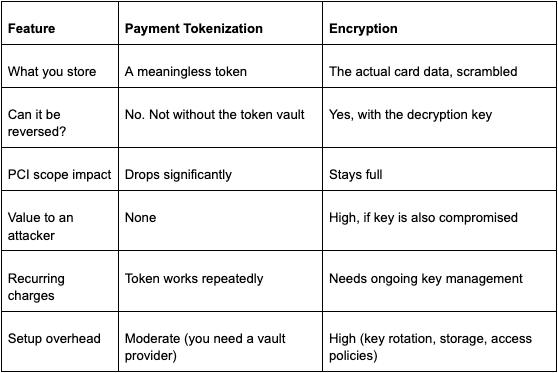
Encryption takes a card number and converts it into unreadable gibberish using a cryptographic key. Straightforward enough. The catch is that the original data still exists underneath. Someone with the right key can reverse the whole process and pull the actual card number back out.
That reversibility is exactly what makes merchants nervous, or at least it should. If attackers get the encrypted data and the key? Game over. No second chance. No fallback mechanism. You’re issuing breach notifications and fielding calls from your acquiring bank. This is precisely the gap that payment tokenization was designed to close.
And then there’s compliance. Because encrypted data is technically still cardholder data (just disguised), your entire infrastructure stays in PCI scope. Every server. Every database. Every employee with access. The audit surface is enormous, and the costs reflect that.
What Makes Payment Tokenization a Different Animal
With payment tokenization, the actual card number never stays in your system. It gets swapped out for a randomly generated string that has absolutely no mathematical connection to the original number. You can’t reverse-engineer it. You can’t decrypt it. There’s nothing to decrypt.
That difference sounds subtle on paper. In practice, it changes your whole compliance posture. Your systems aren’t holding real card data anymore, so a huge chunk of PCI requirements simply stop applying to you. Fewer audits. Lower costs. And if someone breaches your database, they walk away with tokens that are worthless outside your specific ecosystem.
I sometimes explain it like this to merchants who are more visual: encryption is putting your cash in a locked safe inside your office. Payment tokenization is moving the cash to a bank vault across town and keeping a receipt in your desk drawer. Someone breaks into your office? The receipt tells them nothing.
Putting Them Next to Each Other
So Which One Do You Actually Need?
Honestly? Probably both. But not equally.
Encryption handles the transport layer well. When card data moves from a customer’s browser to your payment processor, TLS and AES encryption protect it during that trip. That part isn’t going anywhere anytime soon.
But for stored data? For card-on-file setups, subscriptions, repeat purchases? Payment tokenization is where the real risk reduction lives. You’re not storing anything that can hurt you. Period.
One thing that doesn’t get talked about enough: insurance. Cyber liability underwriters look at what kind of data you hold and how reversible it is. A tokenized environment where no reversible card data exists on your servers? That’s a materially different risk profile. Some merchants have seen premium reductions after migrating to tokenized storage. Not guaranteed across the board, but the logic tracks and the trend is moving that direction.
And compliance costs aren’t trivial either. Merchants handling encrypted cardholder data can face annual PCI audit bills anywhere from $15,000 to north of $50,000 depending on volume and complexity. Tokenization can shrink that scope by 50 to 70 percent. That’s not a rounding error. That’s real money back in your operating budget every single year.
Choosing the Right Approach for Protecting Payment Data
Nobody’s going to tell you to rip out encryption entirely. You shouldn’t. But if you’re a merchant still relying on encryption alone for storing payment credentials, you’re carrying more risk and more cost than you need to.
Payment tokenization isn’t some futuristic upgrade. It’s already the standard for how modern payment stacks handle stored card data. The merchants who figured that out early are spending less on compliance, sleeping better after breach headlines, and running leaner security operations.
The question was never really tokenization versus encryption. It’s about knowing which tool solves which problem and not pretending one covers both.
Disclaimer: This content is for informational purposes only and is not intended as financial advice, nor does it replace professional financial advice, guidance, or recommendations. Always consult with a qualified financial professional before making any financial decisions.